Security Auditor
Two scans: what the internet can already see, and what the code actually does.
The problem
A conventional scanner models a web application. It does not model an application with a language model inside it, where a chat message can reach a shell and model output can reach a database. That whole class of logic flaw only exists once an agent is in the loop, and it is invisible to tools written before agents were.
What we built
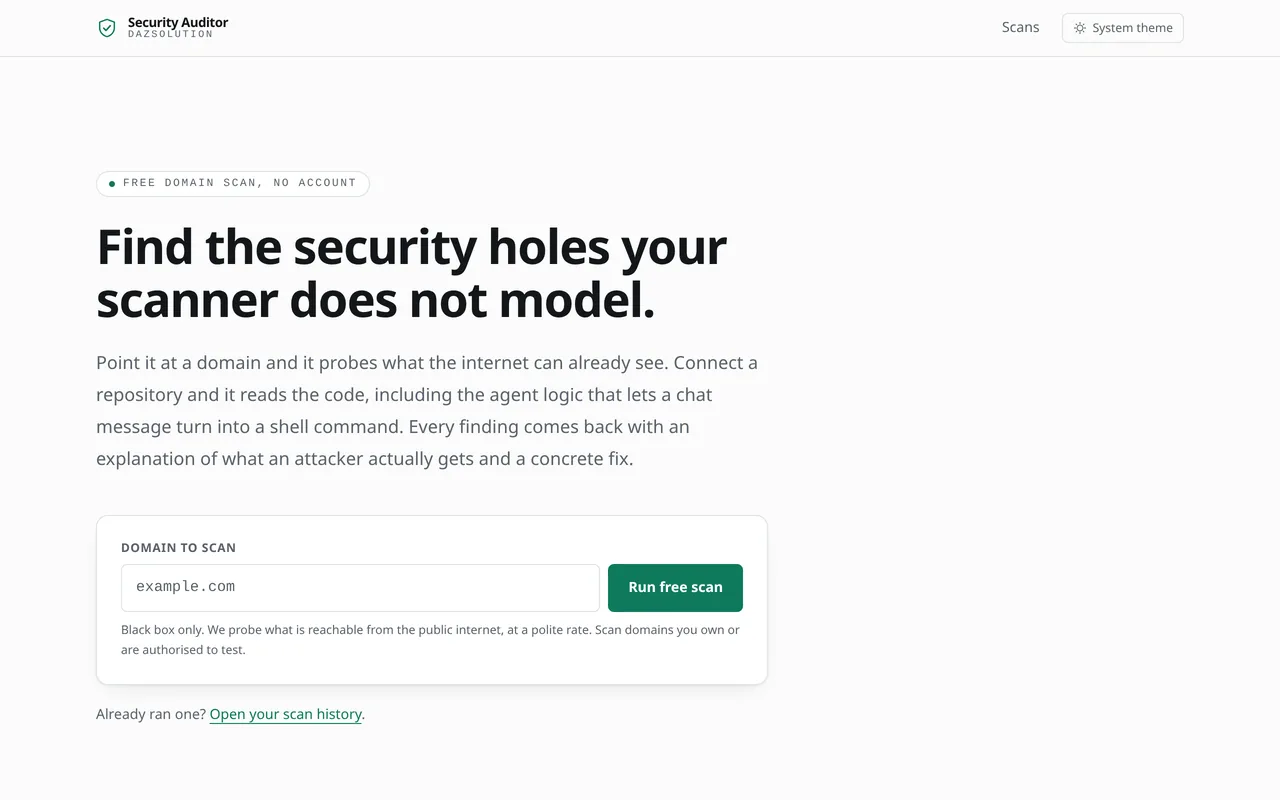
Two tiers that answer different questions. The free tier is black box: point it at a domain and it probes only what is reachable from the public internet, at a deliberately polite rate, with no account. The paid tier is white box: connect a repository and it reads the code, tracing the agent paths specifically, user input arriving at a prompt and model output leaving for a shell.
In the build
- A free domain scan that runs with no account and no card
- Repository scanning that traces prompt and shell paths, not just dependencies
- Every finding explains what an attacker actually gets, then gives a concrete fix
- Per-user scan history, so a domain can be re-checked over time
- Next.js
- React
- FastAPI
- PostgreSQL
- Alembic
- Docker